AWX
1. Informations
1.1. awx1.home.lab
| Caractéristiques | |
|---|---|
| RAM | 6 Go |
| CPU | 4 coeurs |
| Disque | 10 Go + /var/lib/awx 30 Go |
| Hostname | awx1.home.lab |
| IP admin | 192.168.50.27 |
2. Documentations
3. Configuration du réseau
- Modifier le hostname
$ sudo hostnamectl hostname awx1.home.lab
4. Partitionnement
- Formater la deuxième partition
/dev/sdb(30 Go)
$ sudo vgcreate vg1 /dev/sdb
$ sudo lvcreate -n awx -l 100%FREE vg1
$ sudo mkfs -t ext4 /dev/vg1/awx
$ sudo mkdir /data
- Modifier le fichier
/etc/fstab
#/dev/mapper/almalinux-swap none                    swap    defaults        0 0
# AWX
/dev/vg1/awx /data ext4 defaults 0 0
- Désactiver la swap
$ sudo swapoff -a
- Monter la partition
/data
$ sudo systemctl daemon-reload
$ sudo mount -a
- Créer les dossiers nécessaires
$ sudo mkdir -p /data/k3s
$ sudo mkdir -p /data/projects
$ sudo mkdir -p /data/postgres-15
$ sudo ln -s  /data/k3s /var/lib/rancher/k3s
5. Installation de k3s
5.1. Téléchargement du script d'installation
$ sudo -i
# curl -sfL https://get.k3s.io | sh -
5.2. Créer le fichier de configuration ~/.kube/config
- Créer le fichier de config
~/.kube/config
$ mkdir ~/.kube
$ sudo cat /etc/rancher/k3s/k3s.yaml > ~/.kube/config
$ sudo chown $USER ~/.kube/config
$ chmod 0600 ~/.kube/config
$ echo "KUBECONFIG=~/.kube/config >> ~/.bashrc"
$ source ~/.bashrc
- Tester la commande
kubectl
$ kubectl get nodes
ou
$ KUBECONFIG=~/.kube/config kubectl get nodes
5.3. Installation de Kustomize
$ cd /usr/local/bin
$ curl -s "https://raw.githubusercontent.com/kubernetes-sigs/kustomize/master/hack/install_kustomize.sh"  | bash
6. Installation des prérequis
6.1. Installer podman
$ sudo yum install podman
6.2. Installer postgresql
$ sudo yum install postgresql-server postgresql-contrib
$ sudo postgresql-setup --initdb
$ sudo systemctl enable --now postgresql
6.3. Ouvrir les ports sur le firewall
$ sudo firewall-cmd --permanent --add-port=80/tcp
$ sudo firewall-cmd --permanent --add-port=443/tcp
$ sudo firewall-cmd --permanent --add-port=5432/tcp
$ sudo firewall-cmd --reload
6.4. Ajouter le repo "epel-release"
$ sudo yum install epel-release
6.5. Ajouter un utilisateur dédié "awx"
$ sudo useradd -m -d /opt/awx -s /bin/bash awx
$ echo "awx ALL=(ALL) NOPASSWD: ALL" | sudo tee /etc/sudoers.d/awx
$ sudo echo "tz:100000:65536" >> /etc/subuid
$ sudo echo "tz:100000:65536" >> /etc/subgid
$ podman system migrate
6.6. Installer ansible
$ sudo yum install ansible
6.7. Installer awx-cli
$ sudo yum install python3-pip
$ pip3 install ansible-tower-cli --user
$ awx-cli --version
6.8. Installer git et make
$ sudo yum install git make
7. Installation de AWX (version 1)
J'ai eu des problèmes d'installation en me basant sur la documentation officielle : voir au chapitre suivant pour une deuxième méthode d'installation plus facile à réaliser.
7.1. Documentations
7.2. Utiliser le script d'installation de awx-operator
export NAMESPACE=awx
export RELEASE_TAG=`curl -s https://api.github.com/repos/ansible/awx-operator/releases/latest | grep tag_name | cut -d '"' -f 4`

kubectl create ns ${NAMESPACE}

KUBECONFIG=~/.kube/config kubectl config set-context --current --namespace=$NAMESPACE

git clone https://github.com/ansible/awx-operator.git
cd awx-operator
git checkout $RELEASE_TAG

make deploy
cd config/manager
../../bin/kustomize build . | KUBECONFIG=~/.kube/config kubectl apply -f -
ou
kubectl apply -k .
7.3. Vérifier l'installation de AWX Operator
kubectl get pods -n awx
NAME                                               READY   STATUS    RESTARTS   AGE
awx-operator-controller-manager-58b7c97f4b-btrtn   2/2     Running   0          16m
- Changer le namespace par défaut dans le fichier de config
KUBECONFIG=~/.kube/config kubectl config set-context --current --namespace=awx
7.4. Déploiement de AWX via AWX Operator
7.4.1. Création des répertoires
$ sudo mkdir -p /data/projects
$ sudo mkdir -p /data/postgres-13
7.4.2. Déployer awx
$ kubectl apply -f awx-pvc.yml
$ kubectl apply -f awx-pv.yml
$ kubectl apply -f awx-deployment.yml
7.4.3. Vérifier l'installation
$ kubectl get pods -l "app.kubernetes.io/managed-by=awx-operator"
$ kubectl get nodes
NAME            STATUS   ROLES                  AGE    VERSION
awx1.home.lab   Ready    control-plane,master   120m   v1.32.3+k3s1
7.4.4. Récupérer le mot de passe admin
$ kubectl get secret awx-admin-password -o go-template='{{range $k,$v := .data}}{{printf "%s: " $k}}{{if not $v}}{{$v}}{{else}}{{$v | base64decode}}{{end}}{{"\n"}}{{end}}'
8. Installation de AWX (version 2)
J'ai eu des problèmes avec la première tentative d'installation. Voici une deuxième méthode en utilisant le dépôt https://github.com/GiuffreLab/awx-operator
8.1. Supprimer les pods créés précédemment (optionnel)
$ kubectl delete pvc --all
$ kubectl delete pv --all
$ kubectl delete awx awx -n awx
8.2. Récupérer le code-source de GiuffreLab/awx-operator
$ git clone https://github.com/GiuffreLab/awx-operator.git
- Modifier les fichier
kustomization.yaml
kustomization.yaml
apiVersion: kustomize.config.k8s.io/v1beta1
kind: Kustomization
resources:
  # Find the latest tag here: https://github.com/ansible/awx-operator/releases
  - github.com/ansible/awx-operator/config/default?ref=2.19.1
  - awx-manifest.yaml

  # Set the image tags to match the git version from above
images:
  - name: quay.io/ansible/awx-operator
    newTag: 2.19.1

  # Specify a custom namespace in which to install AWX
namespace: awx
- Créer le fichier
awx-manifest.yaml
awx-manifest.yaml
apiVersion: awx.ansible.com/v1beta1
kind: AWX
metadata:
  name: awx1
spec:
  service_type: nodeport
  nodeport_port: 32000    # Adjust the port to the port number you wish
  ingress_type: none
  hostname: awx1.home.lab
  postgres_init_container_resource_requirements: {}
  postgres_data_volume_init: true
8.3. Déployer les pods
- Créer un namespace
awx
$ kubectl create namespace awx
- Déployer les ressources
$ kubectl apply -k .
- Surveiller l'avancée de l'installation de AWX
$ kubectl -n awx logs -f deployments/awx-operator-controller-manager -c awx-manager
$ kubectl get pods -n awx --watch
- Vérifier que l'installation de AWX s'est bien déroulée
$ kubectl get pods -l "app.kubernetes.io/managed-by=awx-operator" -n awx

NAME                             READY   STATUS    RESTARTS   AGE
awx-demo-postgres-13-0           1/1     Running   0          47h
awx-demo-task-68d5bb94fc-46872   4/4     Running   0          47h
awx-demo-web-594cc6c687-bpfqb    3/3     Running   0          47h
- Récupérer le mot de passe admin
kubectl get secret awx-admin-password -n awx -o jsonpath="{.data.password}" | base64 --decode ; echo
- Se connecter sur https://awx1.home.lab
9. Copie du certificat de l'AC interne dans le cluster Kubernetes
J'ai eu un problème car le certificat de mon serveur LDAP n'était pas reconnu par le pod awx-web et l'authentification avec le protocole LDAPS (chiffré) ne fonctionnait.
9.1. Documentation
- https://github.com/ansible/awx-operator/issues/376
- https://paraspatidar.medium.com/add-self-signed-or-ca-root-certificate-in-kubernetes-pod-ca-root-certificate-store-cb7863cb3f87
- https://github.com/kurokobo/awx-on-k3s/blob/main/tips/trust-custom-ca.md
$ cd ~/awx-on-k3s/base
$ cp /etc/pki/ca-trust/source/anchors/ca-homelab.pem cacert.pem
$ kubectl rollout restart -n awx
$ kubectl -n awx logs -f deployments/awx-operator-controller-manager
$ kubectl exec -it awx-web-5465945d6c-qvkmn -n awx -- bash
-
Dans l'interface web d'AWX, aller dans le menu : Settings > Jobs settings > Edit, et modifier les options suvivantes :
- Activer :
Expose host paths for Container Groups. - Vérifier le champ :
Paths to expose to isolated jobscontient :"/etc/pki/ca-trust:/etc/pki/ca-trust:O"
- Activer :
-
Redéployer le pod
awx-web
$ kubectl rollout restart deployment awx-web -n awx
10. Authentification par LDAP
10.1. Ajouter le serveur LDAP
-
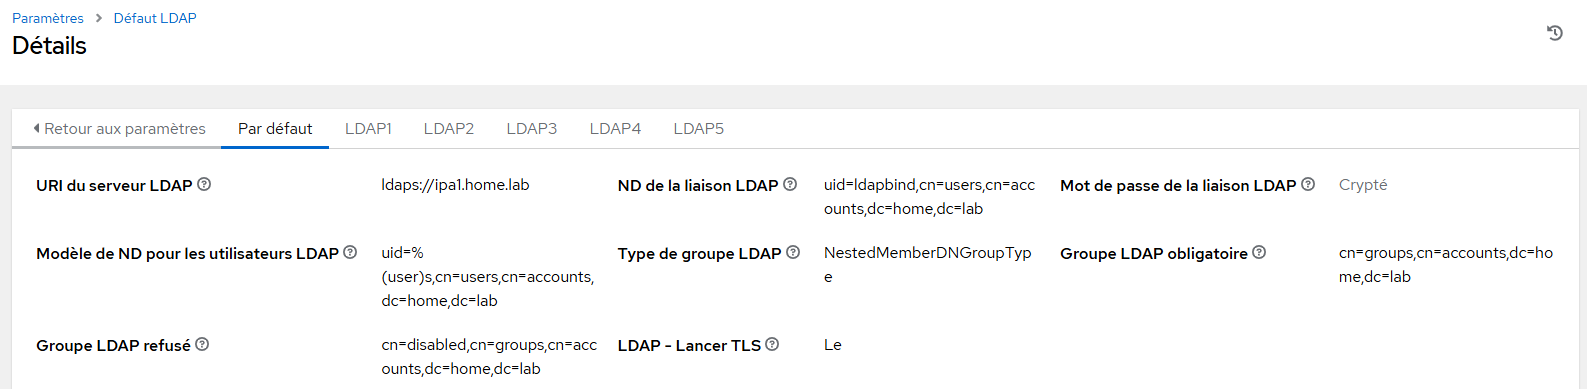
Aller dans le menu Paramètres > Authentification > Paramètres LDAP
-
Editer l'annuaire LDAP par défaut
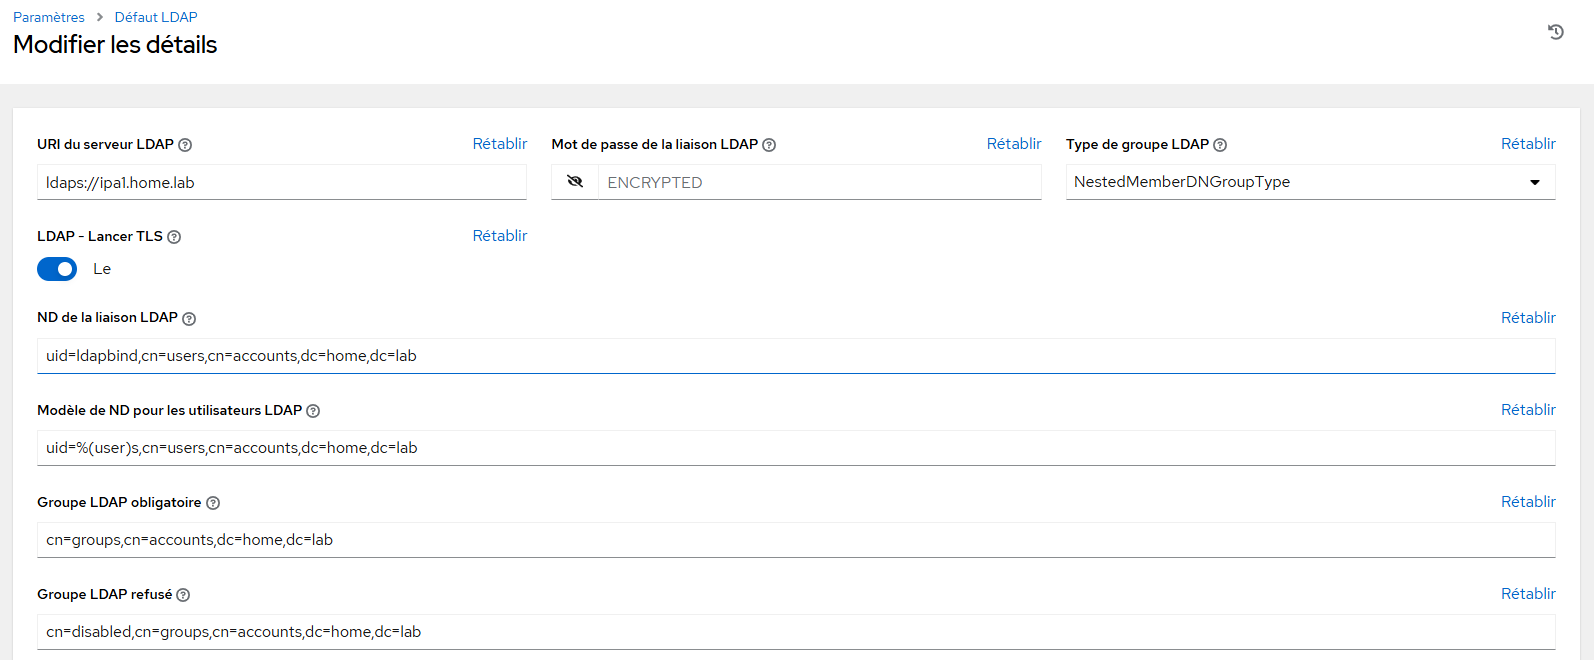
- Recherche d'utilisateurs LDAP
[
  "cn=users,cn=accounts,dc=home,dc=lab",
  "SCOPE_SUBTREE",
  "(uid=%(user)s)"
]
- Recherche de groupes LDAP
[
  "cn=groups,cn=accounts,dc=home,dc=lab",
  "SCOPE_SUBTREE",
  "(objectClass=groupOfNames)"
]
- Mapp des attributs d'utilisateurs LDAP
{
  "email": "mail",
  "first_name": "givenName",
  "last_name": "sn"
}
- Paramètres de types de groupes LDAP
{
  "member_attr": "member",
  "name_attr": "cn"
}
- Résumé du serveur LDAP